Buy news247.eu ?
We are moving the project
news247.eu .
Are you interested in purchasing the domain
news247.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy news247.eu ?
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **
Similar search terms for Iptables
Top-Angebote
Products related to Iptables:
-
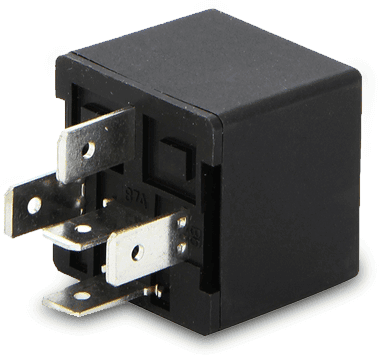
Borsehung B17818 Relay, main currentRelay function: Pre-glow device, X contact relief; Rated Voltage [V]: 12; Number of connectors: 4; Current Strength [A]: 70; Relay Number: 644; Construction Year from: 01/2006, 03/2010, 05/2010, 02/2010, 05/2002, 11/2002, 12/2002, 07/2003, 03/2003, 02/2003, 01/2004, 03/2004, 10/2003, 12/2003, 11/2003, 05/2004, 06/2004, 02/2004, 04/2004, 11/2004, 07/2004, 03/2005, 10/2004, 05/2005, 09/2004, 11/2005, 10/2005, 09/2005, 08/2005, 07/2005, 07/2006, 04/2006, 08/2006, 12/2005, 05/2006, 03/2006, 06/2006, 02/2005, 11/2006, 06/2005, 08/2007, 07/2007, 02/2007, 09/2007, 06/2007, 12/2007, 11/2007, 03/2008, 02/2006, 09/2008, 12/2006, 08/2008, 07/2009, 10/2009, 01/2010, 08/2009, 11/2009, 01/2008, 02/2008, 09/20098,99 £*Shipping: 8,45 £Secure redirect to the provider


-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **

What is the current global language?
English is often considered the current global language. It is the most widely spoken language in the world and is used as a common language for international communication, business, and diplomacy. Many countries teach English as a second language, and it is the primary language of the internet and international travel. As a result, English has become the dominant language for global interactions. **
How does the global ocean current flow?
The global ocean current flows in a complex pattern driven by a combination of factors such as wind, temperature, salinity, and the Earth's rotation. The major ocean currents form large circular patterns called gyres in each of the ocean basins. These currents are influenced by the Coriolis effect, which causes the water to move in a clockwise direction in the Northern Hemisphere and a counterclockwise direction in the Southern Hemisphere. Additionally, the global ocean current is also influenced by the thermohaline circulation, which is driven by differences in water density due to variations in temperature and salinity. Overall, the global ocean current is a dynamic and interconnected system that plays a crucial role in regulating the Earth's climate and transporting heat around the planet. **
Top-Angebote
Products related to Iptables:
-
Current Softflex Dark Blue Grill Cover For Current Model G and Model G 2.0Protect your investment with the Ocean Colored Current Softflex Cover. It is lightweight yet built to withstand the elements and custom sized to fit your Current grill or griddle. Machine washable, and made to last and stylish.99,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Borsehung B17806 Relay, main currentConstruction Year from: 01/2009, 11/1995, 03/2006, 01/1997, 06/2010, 11/1996, 05/2010, 10/1997, 09/1997, 08/1997, 03/2012, 08/2010, 02/2011, 02/2009, 08/2008, 04/2011, 09/2008, 09/1998, 08/1998, 05/2000, 03/2000, 10/1999, 06/2001, 04/2000, 01/2001, 02/2001, 04/2002, 06/2002, 02/2002, 09/2002, 08/2002, 05/2001, 12/2002, 10/2002, 01/2003, 09/2003, 05/2003, 03/2003, 08/2003, 04/2004, 05/2004, 07/2003, 01/2004, 03/2004, 10/2003, 12/2003, 02/2004, 02/2003, 07/2004, 08/2004, 09/2004, 06/2004, 01/2005, 03/2005, 05/2005, 11/2004, 02/2005, 08/2005, 07/2005, 11/2005, 10/2004, 01/2006, 12/2005, 04/2005, 10/2005, 09/2005, 09/2006, 06/2006, 10/2006, 05/2006, 11/2006, 12/2006, 08/2006, 07/2006, 06/2007, 07/2007, 01/2007, 02/2006, 11/2007, 10/2007, 05/2007, 09/2007, 04/2007, 08/2007, 01/2008, 02/2008, 05/2008, 04/2006, 12/2008, 02/2007, 11/2008, 10/2008, 07/2008, 04/2009, 07/2009, 09/2009, 12/2009, 11/2009, 03/2010, 08/2009, 01/2010, 02/2010, 04/2008, 07/20105,99 £*Shipping: 8,45 £Secure redirect to the provider
-
Borsehung B17818 Relay, main currentRelay function: Pre-glow device, X contact relief; Rated Voltage [V]: 12; Number of connectors: 4; Current Strength [A]: 70; Relay Number: 644; Construction Year from: 01/2006, 03/2010, 05/2010, 02/2010, 05/2002, 11/2002, 12/2002, 07/2003, 03/2003, 02/2003, 01/2004, 03/2004, 10/2003, 12/2003, 11/2003, 05/2004, 06/2004, 02/2004, 04/2004, 11/2004, 07/2004, 03/2005, 10/2004, 05/2005, 09/2004, 11/2005, 10/2005, 09/2005, 08/2005, 07/2005, 07/2006, 04/2006, 08/2006, 12/2005, 05/2006, 03/2006, 06/2006, 02/2005, 11/2006, 06/2005, 08/2007, 07/2007, 02/2007, 09/2007, 06/2007, 12/2007, 11/2007, 03/2008, 02/2006, 09/2008, 12/2006, 08/2008, 07/2009, 10/2009, 01/2010, 08/2009, 11/2009, 01/2008, 02/2008, 09/20098,99 £*Shipping: 8,45 £Secure redirect to the provider
-
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
-
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
Similar search terms for Iptables
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **
-
What is the current global language?
English is often considered the current global language. It is the most widely spoken language in the world and is used as a common language for international communication, business, and diplomacy. Many countries teach English as a second language, and it is the primary language of the internet and international travel. As a result, English has become the dominant language for global interactions. **
-
How does the global ocean current flow?
The global ocean current flows in a complex pattern driven by a combination of factors such as wind, temperature, salinity, and the Earth's rotation. The major ocean currents form large circular patterns called gyres in each of the ocean basins. These currents are influenced by the Coriolis effect, which causes the water to move in a clockwise direction in the Northern Hemisphere and a counterclockwise direction in the Southern Hemisphere. Additionally, the global ocean current is also influenced by the thermohaline circulation, which is driven by differences in water density due to variations in temperature and salinity. Overall, the global ocean current is a dynamic and interconnected system that plays a crucial role in regulating the Earth's climate and transporting heat around the planet. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.